Cloud and AI security for regulated companies
Azure, AWS and Google Cloud
We design and build on the main cloud platforms.
Infrastructure as code
The same steps every time, with code, pipelines and clear runbooks.
US-based, remote-first delivery
Senior engineers who work with teams across the US and follow US rules.
Secure Azure, AWS, and Google Cloud foundations in 5 to 10 days. Then AI in production on top.

Frameworks we design to:

Microsoft Azure
Amazon Web Services
Google Cloud
Terraform
Kubernetes
SIEM & SOAR
Built to meet the US rules you follow:
Platform overview

01 Consumers & Apps
Enterprise Developers
- Git repositories & CI triggers
- mTLS & SSH key auth
Business & Portal Users
- Internal apps & client portals
- Browser / web / mobile app
Autonomous AI Agents
- Tool calls, MCP & Copilots
- Scoped API key / OAuth 2.0
02 Edge & Identity
Cloudflare & WAF Armor
- Global edge anycast ingress
- OWASP Top 10 & Layer 7 mitigation
- TLS 1.3 / HTTP/3 termination
Microsoft Entra ID
- Conditional Access policies
- Phishing-resistant MFA / FIDO2
- Workload identity federation
- Zero Trust enforcement
03 Platform Automation
Reusable Landing Zones
- Multi-account Terraform IaC
- Hub-and-spoke mesh network
GitOps CI/CD Pipelines
- ArgoCD & GitHub Actions
- Automated CVE & SAST gates
Unified Observability
- Telemetry & distributed tracing
- Prometheus / Sentinel SIEM
04 Multi-Cloud Estate
Microsoft Azure
- AKS · Azure OpenAI · Fabric
- US East / West & global regions
Amazon Web Services
- EKS · Lambda · S3 encryption
- Zero-egress private subnets
Google Cloud Platform
- GKE · Vertex AI · BigQuery
- us-east4 / us-west1 regions
Continuous Security & Compliance Substrate
Policy-as-code guardrails, real-time posture scanning (CSPM), cryptographic audit logging, and least-privilege telemetry across every tier.
Frameworks: NIST CSF 2.0 · NIST SP 800-53 · CIS Controls · HIPAA · PCI DSS · ISO 27001 · SOC 2 Readiness
Core capabilities
Cloud, security, DevOps and AI, built as one.
Four things we do, and they work best together. Pick the one you need most.
01
Cloud Modernization
Modernize the foundation before you build the skyscraper.Lots of teams are "in the cloud" and still pay for it in the wrong ways. Costs creep up. Setups drift apart. No one owns sign-in or the network. The move stopped halfway. Fast at first, then pain.
Explore capability 02 Cybersecurity & Compliance
Security your team can run, and evidence auditors accept.Cybersecurity and compliance need controls your team can operate and evidence it can retrieve. We connect identity, detection and audit preparation so security work supports daily operations and documented reviews.
Explore capability 03 Platform Engineering
Platform Engineering Strategy and Golden PathsPlatform engineering strategy connects reusable deployment paths, developer experience and platform ownership. Plan which standards your teams need before choosing the implementation services and tools.
Explore capability 04 AI Transformation
Most AI pilots die at the security review. We build the ones that pass.Everyone has an AI proof-of-concept. Almost no one has AI in production doing real work, because the moment it needs access to real systems and data, security says no, and they are usually right to. Open-ended access with no audit trail and no clear owner is not a product. It is a liability.
Explore capability
Cloud platforms
Multi-cloud engineering, matched to the platform you run.
Platform choice depends on the workload, team and existing environment, not a single default stack.
Enterprise AI
Secure enterprise AI, built for real work.
iNET SYSTEMS builds AI agents and Copilot tools that work with your own systems, data, Microsoft 365 and Teams. Each one gets only the access it needs. Nothing is left wide open.
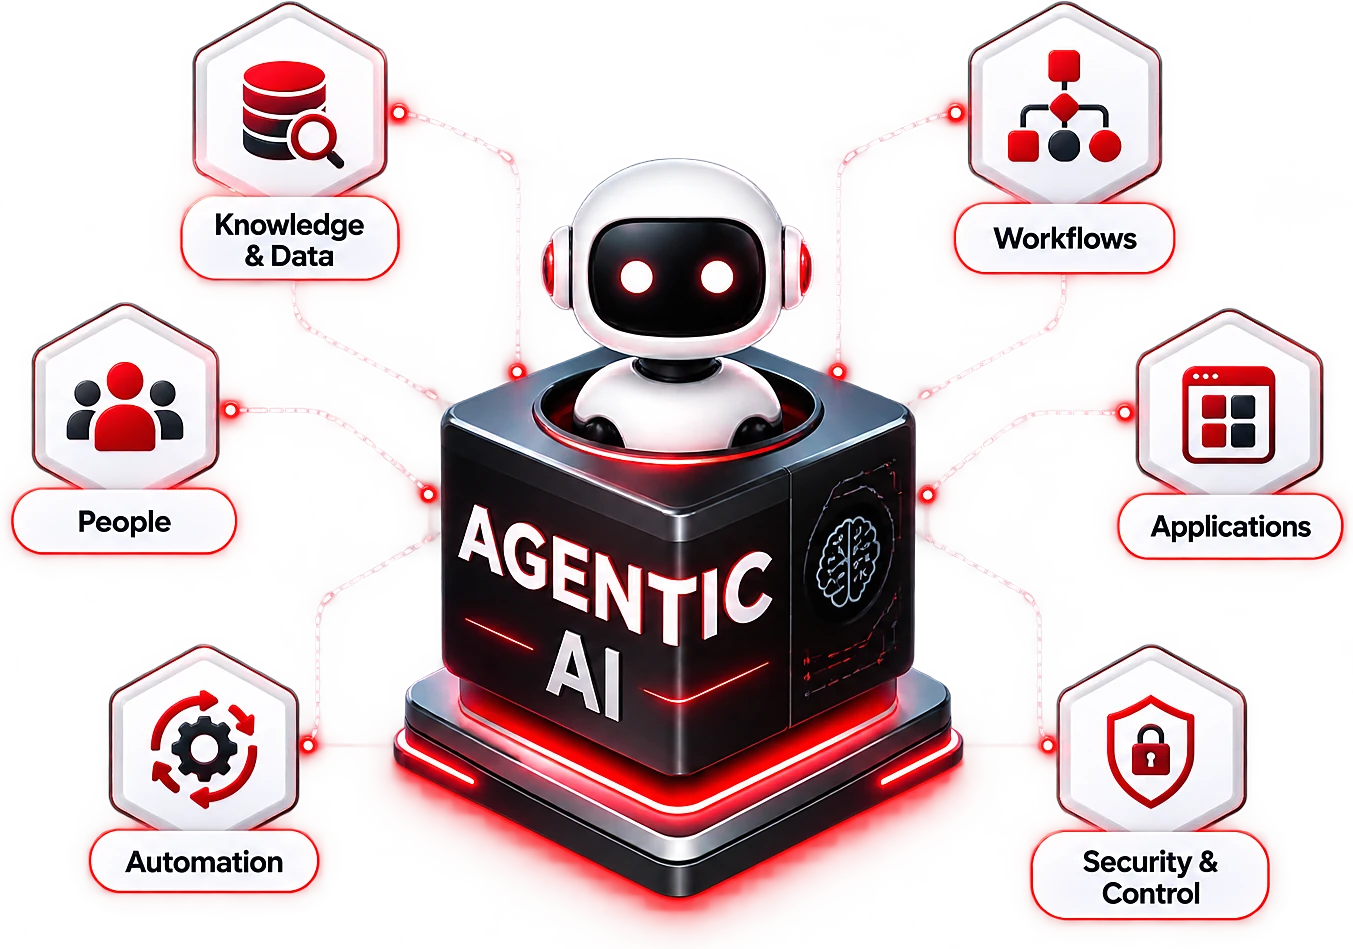
- Agentic AI with governed, least-privilege tool access
- Microsoft AI Foundry and Azure OpenAI implementations
- Microsoft 365 Copilot and Teams integrations
- MCP-based connections to internal APIs and data
- Identity, audit logs and day-to-day monitoring for AI systems
Cybersecurity
Security built in from the start.
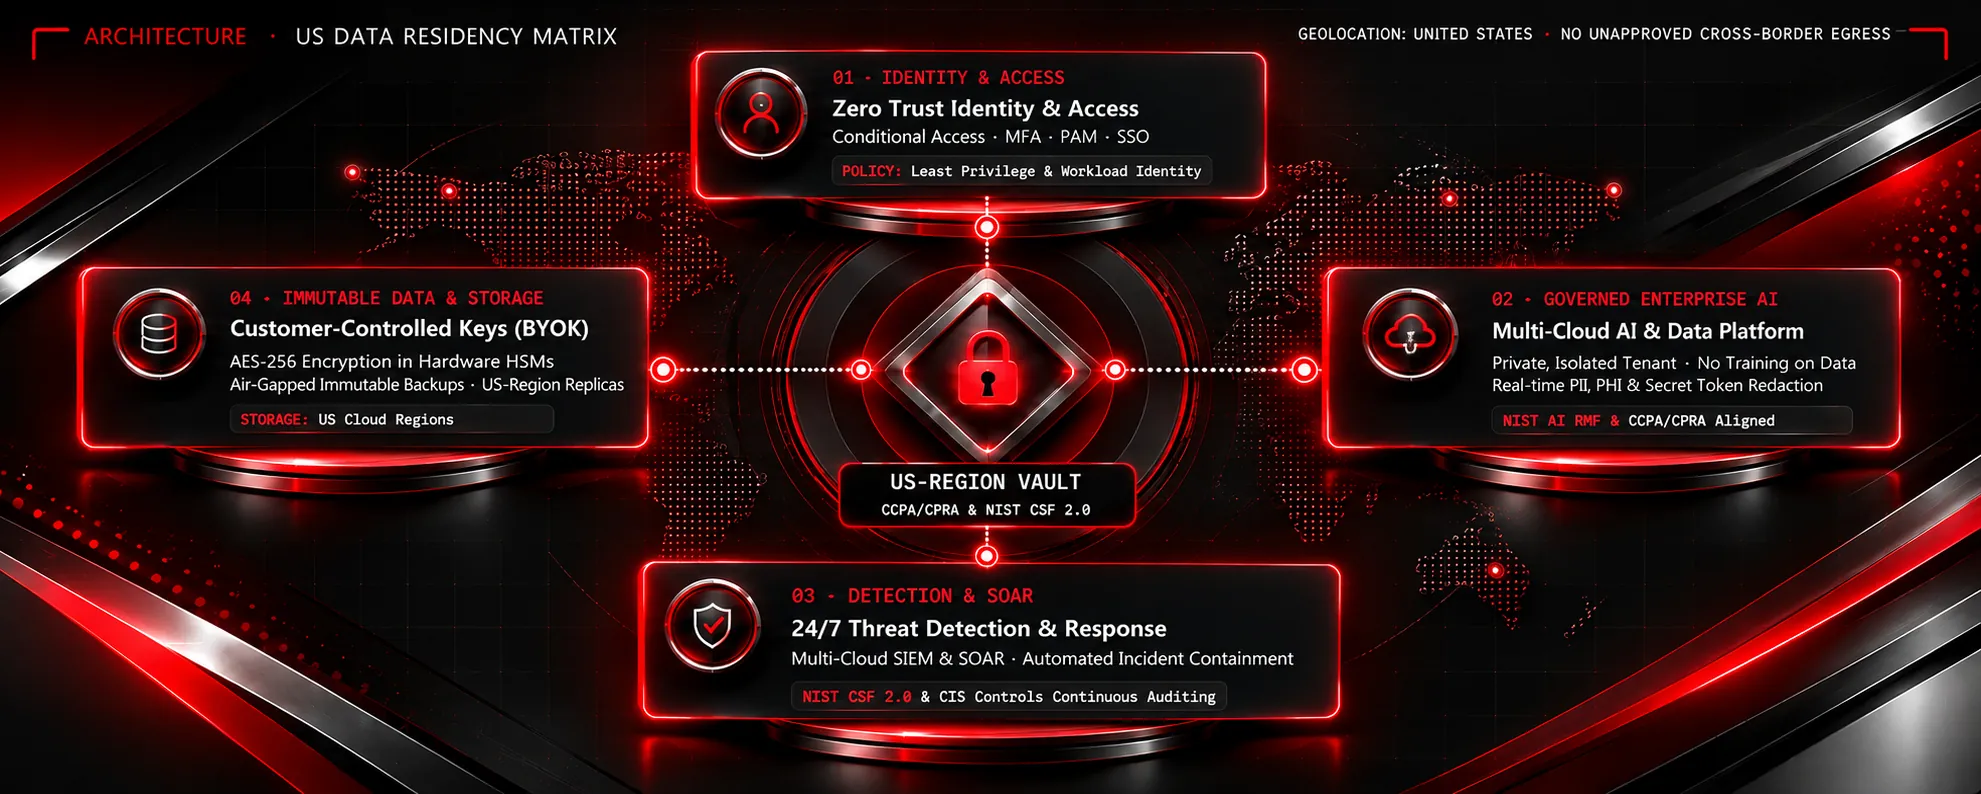
We build security in from the start, not on top at the end. We follow the US rules that apply to you. That means NIST CSF 2.0 and FedRAMP for the public sector, HIPAA for health, PCI DSS and GLBA for banks, SOC 2 for SaaS, and state privacy laws like the CCPA. If your data must stay in the US, we plan for that on day one. With Sentinel, Defender and Entra ID, your team can spot threats, act fast and keep proof for audits.
- Zero Trust identity and least-privilege access
- Microsoft Sentinel and Microsoft Defender for Cloud
- NIST CSF 2.0, SOC 2, HIPAA and PCI DSS-aligned security posture
- US data residency plans for regulated workloads
- Detection tuning and incident response support
US data residency
How we work
From discovery to operation, the work stays accountable.
Every project follows the same clear path, whether it is cloud, security, DevOps or AI.
Discover
We look at your setup, risks and goals before we suggest a thing.
Architect
Plan the target architecture, the controls and the delivery steps before the build starts.
Implement
Build, automate, test and document the solution so it is ready for production use.
Operate and improve
Monitor, support and improve the platform after launch, with clear ownership handed to your team.
Featured case studies
View all case studies
Example projects from recent engagements.
AI Platform | Microsoft Azure
AI agents needed real tools. The security team needed to sleep at night.
AI agents got only the tools they need, through one gateway, with every call logged.
- Least privilegeAccess model
- Entra IDIdentity
Compliance | Cloud Security
SOC 2 shouldn't be a two-week panic before the audit.
Ongoing control checks and repeatable fixes, so you stay ready for SOC 2.
- DefenderSecurity platform
- SOC 2Control model
Cloud Foundation | Multi-Cloud
Every new environment was a snowflake. We made them reproducible.
One cloud base that every team reuses, so new setups are quick and stay in line.
- 3 cloudsCloud scope
- TerraformDelivery model
Technology ecosystem
Used on the main platforms we work with.
We pick the platform that fits your current setup, your risks, your team's skills and how you plan to run it.
Microsoft
Azure
Microsoft 365
Entra ID
Sentinel
Defender
Purview
Copilot
AI Foundry
AWS
EC2
EKS
S3
IAM
VPC
Security Hub
Google Cloud
GKE
Cloud SQL
BigQuery
Cloud Run
Cloud Armor
SecOps
Vertex AI
DevOps
Terraform
Docker
GitHub Actions
Azure DevOps
Kubernetes
Jenkins
AI Engineering
Azure OpenAI
Microsoft AI Foundry
MCP
RAG and vector search
FAQ
Common questions about working with us.
Short answers for teams planning secure Azure, AWS and Google Cloud work.
What does iNET SYSTEMS do?
We design, secure and run cloud, security, DevOps and AI work for regulated US companies on Microsoft Azure, Amazon Web Services and Google Cloud, using infrastructure as code, pipelines and clear runbooks.
Who leads the work?
Adil Pasha leads the work. He spent 25 years securing infrastructure at JPMorgan Chase, Morgan Stanley and Synchrony, from the firewall up to the AI agent.
Where should we start?
Most teams start with the fixed-fee Secure Cloud Foundation Assessment: a read-only review of identity, network, security posture, automation, AI readiness and cost that ends with risk-ranked findings and a 90-day roadmap.
Which compliance frameworks do you design to?
NIST CSF 2.0, SOC 2 and the NIST AI RMF, plus the US rules your sector follows, such as HIPAA, PCI DSS, FedRAMP, CMMC 2.0 and CCPA/CPRA. We design controls to these frameworks; we do not certify compliance.
Can our data stay in the United States?
Yes. If your data must stay in the US, we plan for that on day one and keep it in your own tenant and in approved US regions.
Free first call
Book a 30-minute Call