Cloud sprawl
Subscriptions, accounts and projects grew faster than the structure and controls around them.

Build a Secure, Compliant & AI-Ready Cloud Foundation.
Identify security gaps, strengthen cloud governance, and modernize your Microsoft Azure, AWS or Google Cloud environment with a structured cloud security assessment. Get actionable recommendations across identity, networking, security posture, compliance, and automation.
Clear Security Roadmap
Identify weaknesses and receive prioritized remediation recommendations.
Stronger Cloud Governance
Improve identity, access, networking, and security controls.
Reduced Cloud Risk
Discover configuration gaps and strengthen your security posture.
AI-Ready Infrastructure
Prepare a scalable, governed cloud foundation for future innovation.
It is a cloud security assessment of your Azure, AWS or Google Cloud foundation. We review identity, network, security posture, governance and automation, and find the gaps that put your environment at risk.
In two to three weeks, you get a clear plan to make your cloud secure, automated and ready for AI. Read-only access, a signed NDA and a fixed fee mean no surprises.
 Google CloudPartner
The Microsoft and Google Cloud badges link to our listings in their official partner directories.
Regulated companies already on Azure, AWS, Google Cloud or a mix, facing sprawl, drift, rising costs or a stalled migration.
Subscriptions, accounts and projects grew faster than the structure and controls around them.
What runs in the cloud no longer matches what was designed or approved.
Spend keeps climbing without a clear view of what can be cut safely.
A move to Azure, AWS or Google Cloud is waiting on security and design decisions.
Six areas, reviewed on Azure, AWS, Google Cloud or a mix.
IAM, privileged access, MFA, and least-privilege policies across Entra ID, AWS IAM Identity Center or Cloud Identity.
Related serviceNetwork segmentation, private connectivity, and exposure management, including Kubernetes cluster networking and API gateways.
Related serviceMisconfigurations, security baselines, and posture coverage in Defender for Cloud, AWS Security Hub or Security Command Center.
Related serviceLanding zone structure, policy enforcement, audit readiness, and log coverage in Sentinel, AWS CloudTrail or Google SecOps.
Related serviceTerraform, repeatable deployment patterns, CI/CD, and configuration drift.
Related serviceData access, governance and where AI workloads would sit, with security guardrails in place first.
Related serviceWe agree the scope, set up read-only access and take inventory of your cloud environment and business requirements.
We evaluate identity, networking, configurations, policies, automation and infrastructure architecture.
We rank every gap by risk and impact, and note quick cost wins along the way.
Findings, a target architecture, the 90-day roadmap and an executive readout. Smaller estates finish at the end of week 2.
A session with your leadership to walk through what we found and what to do first.
Cloud architecture and security findings, ordered by risk so you know where to start.
The design your cloud foundation should move toward, for Azure, AWS, Google Cloud or a mix.
An actionable implementation plan with effort estimates for each step.
Where policy, identity and logging controls fall short of the standards you follow.
Automation gaps, AI readiness and quick cost wins found during the review.
Hands-on Azure, AWS and Google Cloud security expertise, led by a practitioner who has run infrastructure in regulated enterprises.
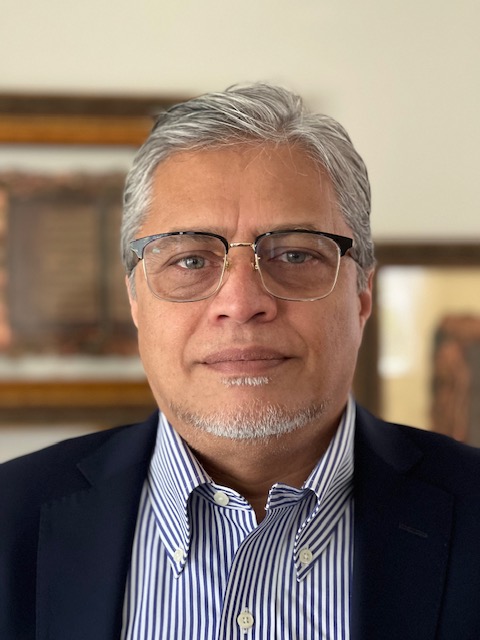
Adil Pasha, 25 years in enterprise infrastructure and security, including JPMorgan Chase, Morgan Stanley and Synchrony. Our certified engineers support the technical review.
Adil leads the assessment and the executive readout.
View our listing in the official partner directory.
View our listing in the official partner directory.
An NDA is signed before we look at anything. We do not change your environment during the assessment.
One fixed fee. You own the findings and the roadmap, and can close the gaps with your team, another partner or us.
A structured review of how your cloud is set up and secured. We check identity, networking, security posture and automation against good practice, then rank the gaps by risk.
Seven review areas: landing zone structure, identity and access, network design, security posture, automation maturity, AI readiness and quick cost wins. You receive risk-ranked findings, a target reference architecture, a 90-day roadmap and an executive readout.
Two to three weeks from kickoff, depending on the size of your estate. Smaller estates finish at the end of week 2.
Yes. We review Azure subscriptions, Entra ID and Conditional Access, network design, Defender for Cloud and Microsoft Sentinel coverage, and Azure Policy.
Yes. We review Google Cloud projects, Cloud Identity, network design, and Security Command Center and Google SecOps coverage.
Yes, with the same depth as Azure and Google Cloud. We review AWS accounts and Organizations, IAM and IAM Identity Center, VPC design, Security Hub and GuardDuty coverage, and CloudTrail logging. We can assess Azure, AWS, Google Cloud, or a mix.
We review your identity, logging and policy controls against NIST CSF 2.0 and note gaps against the rules you follow, such as SOC 2, HIPAA or GLBA. The assessment does not certify compliance.
Read-only access, granted after an NDA is signed. We do not change your environment during the assessment.
Adil Pasha leads the assessment and the executive readout. Certified engineers on our team support the technical review.
You own the findings and the roadmap. You can close the gaps with your team, another partner or us.
Book a 30-minute scoping call. We confirm the scope, timeline and fixed fee before any work begins.
Start with a 30-minute scoping call. You get the scope, timeline and fixed fee before any work begins.
Questions are not stored. Avoid sharing confidential information. Privacy Policy