Fragmented environments
Cloud accounts, subscriptions and projects grow without a consistent identity, networking or policy model.
"Cloud services" covers a lot, so here's how we think about it: strategy and architecture first, a governed foundation second, migration onto it third, and operations to keep it healthy fourth. Skip the early steps and you get the expensive, drifting environment most teams end up regretting. We don't skip them.
Accounts set up in different ways, traffic leaving the network unchecked, settings that drift and bills no one planned for.
Cloud accounts, subscriptions and projects grow without a consistent identity, networking or policy model.
Teams need modernization without downtime, unclear rollback plans or unexpected security exposure.
Spend increases when governance, observability, backup posture and FinOps are not connected.
We design cloud environments that are scalable, governed, observable and repeatable through infrastructure as code. The result is a modernization foundation your teams can operate confidently after launch.
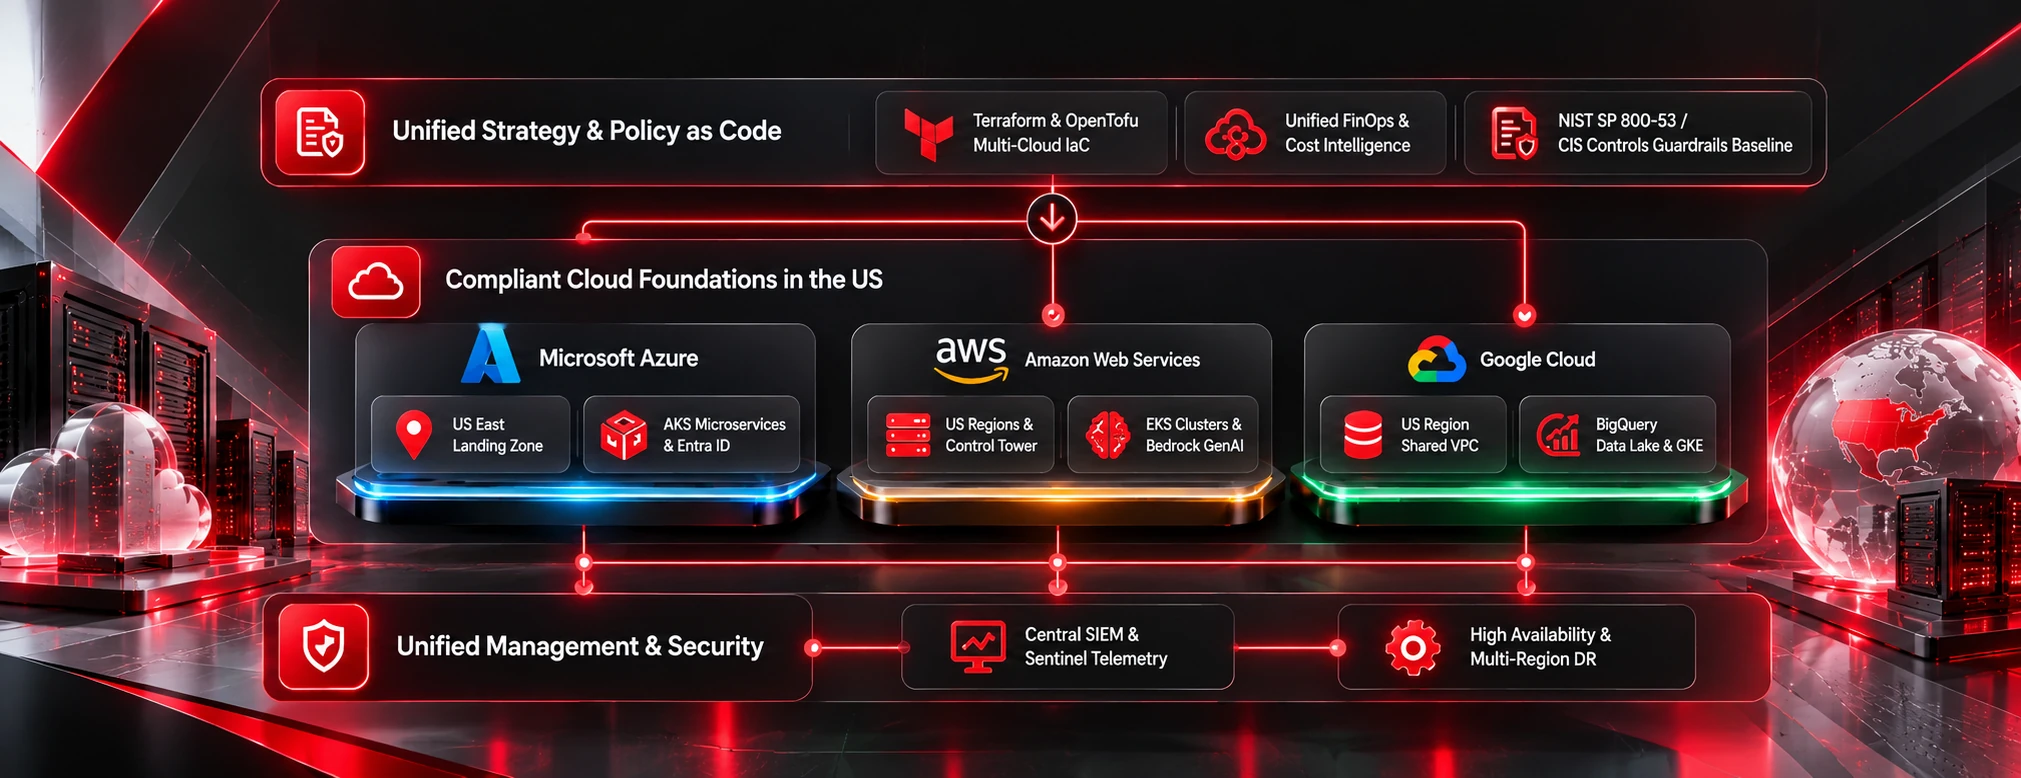
Standardized, production-grade cloud foundations across Azure, AWS, and GCP with identity federation, automated guardrails, and central logging.
Structured 6-R methodology (Rehost, Replatform, Refactor) with migration wave automation and near-zero downtime cutover.
Containerize legacy monolithic apps onto managed Kubernetes (AKS, EKS, GKE) and serverless architectures.
Centralized cloud cost intelligence, automated anomaly alerts, reservation planning, and waste elimination.
US data residency baselines aligned with NIST SP 800-53, CIS Controls, and NIST Privacy Framework regulations.
Modular Terraform/OpenTofu codebases and CI/CD pipelines stored directly in your repositories with zero vendor lock-in.
Built with automatic guardrails, a hub-and-spoke network, rules written as code and one central place for logs.
Inventory current workloads, dependencies and constraints before any migration or design work begins.
Define identity, networking, policy and governance so every environment starts from the same secure baseline.
Build environments as reviewed, version-controlled code instead of manual console changes.
Move workloads on a sequenced plan with rollback options, not a single high-risk cutover.
Hand over monitoring, cost visibility and runbooks so the platform keeps improving after go-live.
Each step ends with a written result and a clear yes or no before the next one starts.
We review each workload, build with Terraform, move it with a way back if needed, and then tune the cost.
Inventory current systems, constraints, risk, cost and migration readiness.
Define architecture, controls, operating model and delivery milestones.
Use infrastructure as code, CI/CD and documentation so environments can be reproduced.
Tune reliability, cost, security and team handover after launch.
Ship new features faster on a cloud that meets your rules, with data kept in the US.
Reusable landing zones make compliant environments faster to reproduce.
Monitoring, backup, policy and runbooks are built before production handover.
Teams understand who owns platforms, workloads, security controls and improvement cycles.
The main cloud providers and automation tools, proven on systems that must stay up.
One cloud base that every team reuses, so new setups are quick and stay in line.
Read the storyShort answers on design choices, timelines and who runs what.
Depends on your workloads, team skills and existing contracts. We'll give you an honest recommendation, not a default.
Yes, most engagements start by improving what's already there.
Questions are not stored. Avoid sharing confidential information. Privacy Policy