Enterprises Adopting AI
For organizations preparing to deploy Copilot and AI agents securely.

Know what your AI can reach before your auditors do.
Identify security risks, uncover critical gaps, and build a clear roadmap for secure AI adoption.
Designed for organizations adopting Microsoft Copilot, Azure AI, Amazon Bedrock, Google Gemini Enterprise Agent Platform, and enterprise AI agents.
For organizations preparing to deploy Copilot and AI agents securely.
For businesses operating across Microsoft 365, Azure, AWS, and Google Cloud environments.
For organizations requiring stronger security governance, compliance, and audit readiness.
This AI security assessment is for teams whose Copilot or AI agent rollout is waiting on security. Copilot and AI agents are only as safe as the permissions behind them. In three weeks, we map what your AI tools can access, find the gaps that would stop a security review, and give you a clear plan to reach production.
What sensitive data Copilot or your agents can surface.
What each agent and app is allowed to read and do.
Authentication, scoping and logging.
Hosting security for AI workloads.
Identity and Conditional Access gaps.
Whether AI activity is logged well enough to audit.
Mapping to NIST AI RMF and the rules that apply to you, such as GLBA, SOC 2 or HIPAA.
Interviews with your CISO, AI lead, identity team and Microsoft 365 or Google Workspace admins. We review AI use cases, identity, data classification, labels and sharing settings.
We assess the seven areas above, from what your AI can surface to how it maps to NIST AI RMF and the rules that apply to you.
Risk-ranked findings, a target governance architecture, the 90-day roadmap and the executive readout.
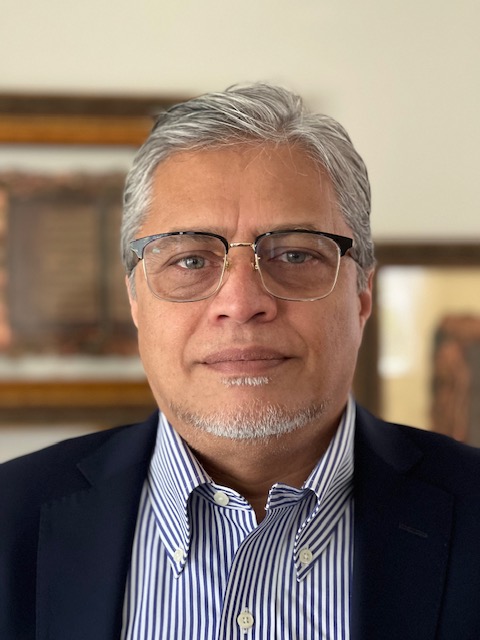
Adil Pasha, 25 years in enterprise infrastructure and security, including JPMorgan Chase, Morgan Stanley and Synchrony. Our certified engineers support the technical review.
Adil leads the assessment and the executive readout.
An NDA is signed before we look at anything. We do not change your environment during the assessment.
One fixed fee and a three-week timeline from kickoff, when interviews and access are scheduled in week 1.
We assess Copilot and Microsoft Foundry agents, Amazon Bedrock agents and Amazon Q Business, and Gemini Enterprise and agents built on Google Cloud.
You own the findings and the roadmap. You can close the gaps with your team, another partner or us.
Read-only access, granted after an NDA is signed. We do not change your environment during the assessment.
Adil Pasha leads the assessment and the executive readout. Certified engineers on our team support the technical review.
Three weeks from kickoff, when interviews and access are scheduled in week 1.
Yes. We assess Copilot and Microsoft Foundry agents, and Gemini Enterprise and agents built on Google Cloud.
Yes, with the same depth as Microsoft and Google Cloud. We assess Amazon Bedrock agents and Amazon Q Business, the IAM roles and permissions behind them, and CloudTrail logging.
You own the findings and the roadmap. You can close the gaps with your team, another partner or us.
Start with a 30-minute scoping call. You get the scope, timeline and fixed fee before any work begins.
Questions are not stored. Avoid sharing confidential information. Privacy Policy