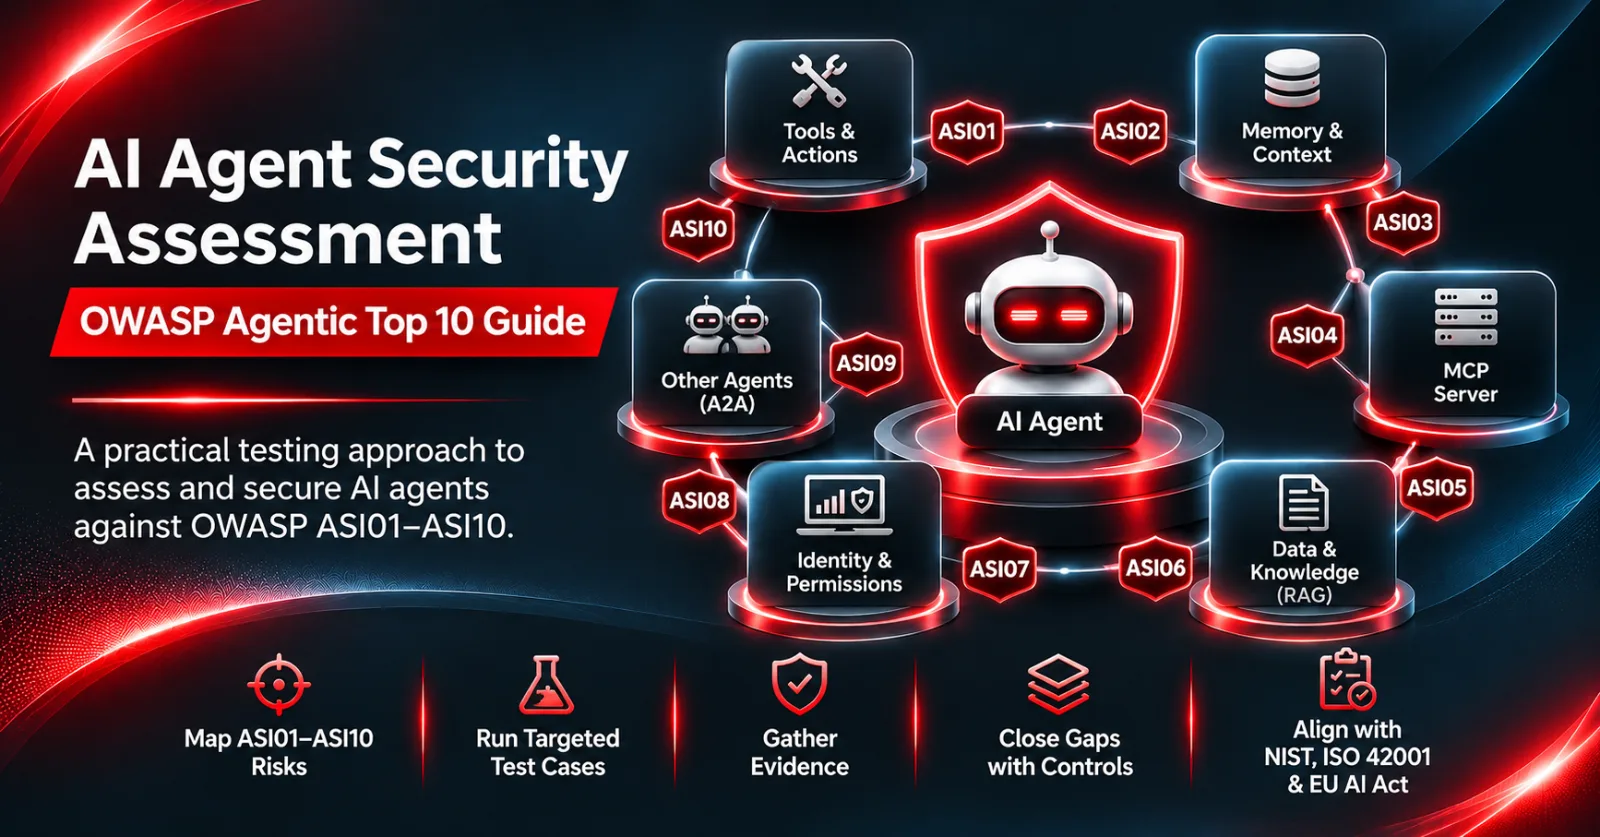
Key takeaway: An artificial intelligence (AI) agent security assessment tests what an autonomous agent can actually do with its tools, identity, memory and connections, not just what its model says. The most useful 2026 baseline is the Open Worldwide Application Security Project (OWASP) Top 10 for Agentic Applications (ASI01-ASI10). Map every agent to those ten risks, test each one, and fix identity and tool scope first.
In recent weeks, a Model Context Protocol (MCP) server compromise at German host Mittwald exposed 56 customer projects, and a flaw in the OpenCode agent let a malicious MCP server run code during sign-in. A traditional pen test would have missed both. That is why we now scope every AI agent security assessment against the OWASP Agentic Top 10 rather than a generic large language model (LLM) checklist.
This guide covers the test cases. For the governance program around them, see our agentic AI governance framework.
What is an AI agent security assessment?
An AI agent security assessment is a structured test of an autonomous AI system’s tools, permissions, memory, data sources and agent-to-agent links to find ways an attacker could make it act against its owner. It differs from an LLM red team because the target is the agent’s actions, not only its text output.
A chatbot that says something wrong is a reputational problem. An agent that deletes a production table, emails a customer list or approves a payment is an incident. The assessment therefore starts from the blast radius: what can this agent reach, under whose identity, and who checks it before it acts?
In practice, every engagement we run covers four surfaces:
- Identity: the service principal, workload identity or application programming interface (API) key the agent runs as, and what identity and access management (IAM) grants it.
- Tools: every function, API, MCP server and plug-in the agent can call, including parameters it controls.
- Context: prompts, retrieved documents (RAG), long-term memory and anything an outsider can write into them.
- Coordination: other agents, orchestrators and humans the agent sends to or takes instructions from.
Why use the OWASP Agentic Top 10 as the baseline?
Because it is the first peer-reviewed risk list written specifically for autonomous agents, and boards and auditors already recognize the OWASP name. The OWASP GenAI Security Project released the Top 10 for Agentic Applications on December 9, 2025.
The older OWASP Top 10 for LLM Applications still matters for prompt injection and output handling. But it was written for chat-style apps. The agentic list adds the risks that only appear once a model can plan, call tools and remember: goal hijack, tool misuse, identity abuse, cascading failures and rogue behavior.
The ecosystem is moving fast around it. On November 5, 2026, Microsoft announced general availability of Defender discovery of local AI agents and their configured MCP servers on Windows and macOS. On November 10, 2026, Cisco said it is adding red teaming of AI applications and agents to AI Defense. Tooling is catching up; your test plan should not wait for it.
How do you test each ASI risk?
You test each risk by trying to make the agent misuse a real capability in a staging copy of its environment, then recording whether a control stopped it. The table below is the matrix we use; risk names follow the OWASP list as summarized by Giskard.
| OWASP ID | Risk | What we test | Evidence to collect | Primary control |
|---|---|---|---|---|
| ASI01 | Agent Goal Hijack | Indirect prompt injection via documents, emails, tickets and web pages the agent reads | Transcript showing changed objective; tool calls made | Input isolation, instruction hierarchy, human approval on high-impact actions |
| ASI02 | Tool Misuse and Exploitation | Can a legitimate tool be steered to an illegitimate outcome (bulk export, delete, send)? | Tool call logs with parameters | Per-tool allow-lists, parameter validation, rate limits |
| ASI03 | Identity and Privilege Abuse | Does the agent have its own identity? Can it act with a user’s or admin’s rights? | IAM policy export, token scopes | Dedicated workload identity, least privilege, short-lived tokens |
| ASI04 | Agentic Supply Chain | Unpinned MCP servers, plug-ins, models and prompt templates loaded at runtime | Inventory with versions and hashes | Signed and pinned components, private registry |
| ASI05 | Unexpected Code Execution | Can generated code or shell commands escape the sandbox? | Sandbox escape attempts, egress logs | Isolated execution, no default network, deny-by-default egress |
| ASI06 | Memory and Context Poisoning | Plant false facts in retrieval-augmented generation (RAG) sources or long-term memory; check later sessions | Before/after answers, memory write logs | Write controls on memory, source provenance, time-to-live values (TTLs) |
| ASI07 | Insecure Inter-Agent Communication | Spoof, replay or tamper with messages between agents | Captured messages, auth headers | Mutual authentication, signed messages, schema validation |
| ASI08 | Cascading Failures | Inject one bad output and watch downstream agents | Failure propagation trace | Circuit breakers, step budgets, output validation between hops |
| ASI09 | Human-Agent Trust Exploitation | Does the agent pressure or mislead approvers into unsafe clicks? | Approval user interface (UI) screenshots, wording | Clear action previews, friction on irreversible steps |
| ASI10 | Rogue Agents | Does behavior drift from scope over long runs or after updates? | Behavioral baselines, anomaly alerts | Runtime monitoring, kill switch, scoped autonomy |
Where the recent MCP incidents fit
Both incidents land squarely in this matrix. According to The Hacker News, OpenCode versions 1.0.137 to 1.18.32 passed an MCP server’s authorization uniform resource locator (URL) unescaped into a PowerShell command on Windows and Windows Subsystem for Linux (WSL), which is ASI04 plus ASI05. The fix shipped in version 1.18.33.
In Mittwald’s case, as summarized here from the company’s own disclosure, attackers read user session tokens through a vulnerable MCP server and used them to reach 56 customer projects. That is ASI03 and ASI04: identity and supply chain.
Which agent risks should you fix first?
Fix identity and tool scope first, because they cap the damage of every other risk. If a hijacked agent can only read one table with a 15-minute token, goal hijack becomes a nuisance rather than a breach.
This is the remediation order we recommend to chief information security officers (CISOs):
- Inventory every agent and MCP server. You cannot assess what you cannot see. Include developer laptops, where coding agents now run with local credentials.
- Give each agent its own identity (ASI03). No shared keys, no borrowed user sessions. Apply Zero Trust: verify every call, assume breach. See Entra ID and identity security.
- Shrink tool scope (ASI02). Remove unused tools; split read and write tools; validate parameters server-side.
- Pin and sign the supply chain (ASI04). Approved MCP registry, version pinning, hash checks in CI/CD.
- Sandbox code execution (ASI05). Deny-by-default egress from any runtime that executes generated code.
- Gate irreversible actions (ASI01, ASI09). Human approval with a plain-language preview for payments, deletions and external sends.
- Protect memory and inter-agent channels (ASI06, ASI07). Authenticated writes, signed messages, provenance tags.
- Add runtime guardrails and a kill switch (ASI08, ASI10). Step budgets, anomaly alerts into your security information and event management (SIEM) (for example Microsoft Sentinel), and a tested way to stop an agent mid-run. Our guide to runtime controls for AI agents covers this step in depth.
“Most agent findings we see are not exotic model attacks. They are old identity mistakes in a new costume: an agent running as a human admin, a long-lived token in a config file, an MCP server nobody pinned. Fix the identity layer and half of the OWASP Agentic Top 10 shrinks overnight.”
iNET SYSTEMS AI Practice
How does the assessment map to NIST AI RMF, ISO 42001 and the EU AI Act?
An agent assessment produces the evidence that governance frameworks ask for. Our NIST Special Publication (SP) 800-53 control map for AI agents shows which controls it tests. It sits in the Measure function of the NIST AI RMF and supports the risk-assessment and operational controls of ISO/IEC 42001.
| Framework | Where the assessment fits | What the auditor wants to see |
|---|---|---|
| National Institute of Standards and Technology (NIST) AI Risk Management Framework (AI RMF) 1.0 | Map (inventory, context) and Measure (testing) functions | Documented test methods, results and residual risk |
| International Organization for Standardization and International Electrotechnical Commission (ISO/IEC) 42001:2023 | AI risk assessment and AI system impact assessment | Repeatable process, records, corrective actions |
| European Union (EU) AI Act | Accuracy, robustness and cybersecurity duties for high-risk systems | Technical documentation and testing evidence |
| OWASP Agentic Top 10 | Test catalog | Coverage of ASI01-ASI10 per agent |
The EU timeline shifted this year. Under the Digital Omnibus on AI, Regulation (EU) 2026/1744, which entered into force on July 27, 2026, stand-alone (Annex III) high-risk obligations now apply from December 2, 2027 and product-embedded (Annex I) ones from August 2, 2028, according to the AI Act Explorer and a Cloud Security Alliance (CSA) research note. That is extra runway, not a reprieve. For the governance side, see our EU AI Act and ISO 42001 crosswalk for agentic AI governance.
What does a good assessment report contain?
A good report lets a chief information security officer (CISO) decide in one meeting what to fix, who owns it and by when. Anything longer than that belongs in an appendix.
We structure every report the same way:
- Agent inventory: each agent, its owner, identity, tools, data classes and autonomy level.
- ASI coverage matrix: pass, partial or fail for ASI01-ASI10 per agent, with evidence links.
- Top five findings: each with exploit path, business impact and a fix that fits in a sprint.
- Control roadmap: 30, 60 and 90-day actions mapped to NIST AI RMF and ISO 42001 clauses.
- Retest plan: which tests become automated checks in the continuous integration and continuous delivery (CI/CD) pipeline so regressions surface before release.
Run the assessment before go-live and again after any material change: a new tool, a new model version or a new data source. Agents change faster than annual pen-test cycles. Our protected health information (PHI) agent blueprint shows these controls in a real healthcare design.
Book an AI agent security assessment
Running agents in production, or about to? iNET SYSTEMS will map your agents to the OWASP Agentic Top 10, test them in a safe staging environment and hand you a prioritized 90-day fix plan. Book an AI agent security assessment or explore our AI governance services.
