
 Azure OpenAI
Public Endpoint Data Exposure
Inference APIs exposed to the public internet risk credential theft, DDoS attacks, and unauthorized data extraction.
Azure OpenAI provides state-of-the-art foundation models with enterprise-grade protection: private VNet routing, zero data retention for training, and Azure-native Entra ID authentication. We architect production generative AI platforms where proprietary data remains within your data boundary, token expenditure is strictly governed, and RAG pipelines deliver factual, grounded responses without exposing sensitive records.
Moving AI from fragile prototypes to governed production requires solving data boundary security, token economics, and model auditability upfront.
Inference APIs exposed to the public internet risk credential theft, DDoS attacks, and unauthorized data extraction.
Ungrounded LLMs invent internal policies or provide incorrect answers to critical customer questions.
Unmonitored chat applications consume excessive tokens without rate-limiting, exceeding operating budgets.
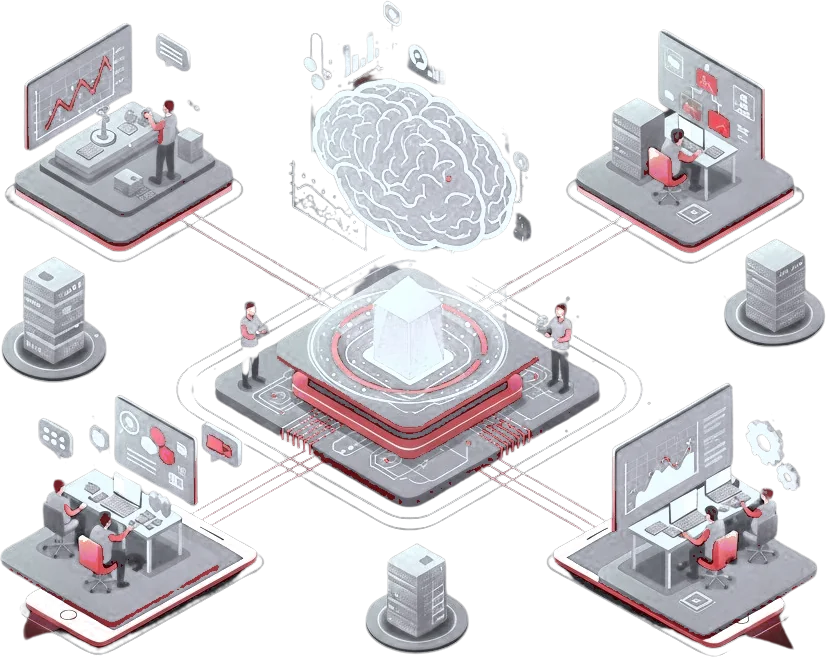
We architect production generative AI platforms where proprietary data remains within your data boundary, token expenditure is strictly governed, and RAG pipelines deliver factual, grounded responses without exposing sensitive records.
Eliminate public internet endpoints entirely by routing all inference traffic over Azure Private Endpoints and internal express routes.
Authenticate client applications and indexing services using Microsoft Entra ID managed identities, eliminating credential leakage.
Combine dense vector search with lexical BM25 matching and semantic re-ranking to deliver highly accurate, grounded answers.
Deploy customized Azure AI Content Safety filters to block jailbreak attempts, toxic content, and unauthorized topics.
Model latency and cost dynamics to select between Provisioned Throughput Units (PTU) for guaranteed SLAs or Pay-as-you-go.
Evaluate and optimize prompts for your domain vocabulary, formal enterprise communication, and industry-specific technical dialect.
We establish isolated network boundaries, least-privilege tool access via MCP, identity enforcement, and comprehensive audit telemetry before launch.
Understand the business goal, current environment, risks and constraints before any design work begins.
Design the target operating model, controls and integration points so the solution fits how the business actually runs.
Build and configure the solution using repeatable, reviewed engineering practices, not one-off manual work.
Test against real scenarios and security requirements before anything reaches production.
Hand over documentation, runbooks and support so the client team can run the result with confidence.
Every phase ends with a documented deliverable and a clear go/no-go decision before the next one starts.
Every milestone validates accuracy, latency, safety guardrails and regional data residency before widening organizational access.
Provision private virtual networks, configure DNS zones, and establish Private Endpoints for zero public exposure.
Design document chunking strategies, generate embeddings, and build hybrid search indexes in Azure AI Search.
Implement Azure AI Content Safety filters, system message guardrails, and test against jailbreak vectors.
Benchmark concurrency, model token consumption curves, and configure rate-limits and budget alerts.
Connect downstream applications via APIM, establish latency dashboards in Application Insights, and transfer runbooks.
Equip enterprise workflows with verified intelligence without exposing sensitive enterprise data or falling out of regulatory compliance.
End-to-end network isolation ensures zero public IP access to your models and vector indexes.
Every generated answer cites specific enterprise documents with direct reference links and confidence scores.
Optimized chunking and semantic caching deliver high-throughput responses under strict SLA targets.
Industry-standard AI platforms engineered for predictable inference latency, high security, and regional data residency.
AI agents got only the tools they need, through one gateway, with every call logged.
Read the storyDirect answers regarding model evaluation, security boundaries, and production readiness.
No. Under Microsoft enterprise licensing and terms of service, your data, prompts, and completions are never accessible to other customers, never used to train base foundation models, and are stored within your private subscription boundary.
We deploy Azure OpenAI with Customer-Managed Keys (CMK) stored in your local Azure Key Vault. Data processing is kept within authorized regional zones, and sensitive personal identifiers are tokenized or masked prior to model ingestion to ensure full compliance with the CCPA/CPRA.
Pay-As-You-Go charges per token consumed and shares infrastructure with other tenants, meaning latency can fluctuate during peak hours. PTUs allocate dedicated, reserved inference capacity with guaranteed latency SLAs and predictable monthly pricing, ideal for high-volume enterprise systems.
We implement defense-in-depth: Azure AI Content Safety Prompt Shields inspect incoming prompts before they reach the model, system prompts are hardened with immutable operational boundaries, and outputs are scanned for sensitive information before returning to the user.
Questions are not stored. Avoid sharing confidential information. Privacy Policy