
 MCP Development
Direct production access
Tools and agents connect straight to production systems with no mediation layer.
MCP is how you give an AI controlled access to tools and data without handing over raw credentials. We build custom MCP servers that expose exactly the operations an agent needs (read this, write that, nothing more) with authentication, scoping and logging built in. It's the difference between a governed integration and a dangerous one.
Moving AI from fragile prototypes to governed production requires solving data boundary security, token economics, and model auditability upfront.
Tools and agents connect straight to production systems with no mediation layer.
One-off integrations are built without consistent access control or logging.
Any connected agent can reach more tools than its task actually requires.
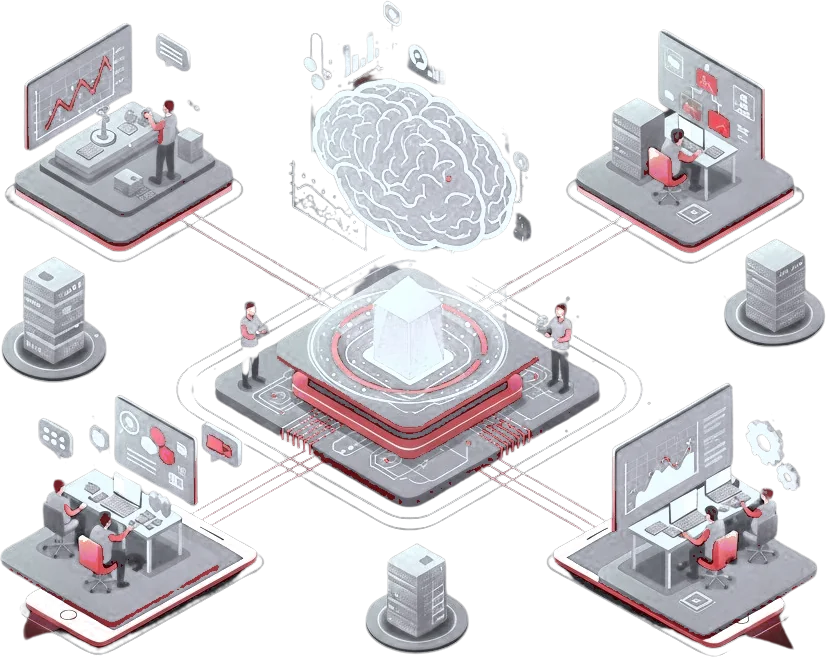
We build custom MCP servers that expose exactly the operations an agent needs (read this, write that, nothing more) with authentication, scoping and logging built in. It's the difference between a governed integration and a dangerous one.
Define exactly which tools, APIs and data the server exposes, and their schemas.
Build connectors to your existing systems instead of requiring a rebuild.
Scope every tool call so agents reach only what their task requires.
Log tool usage so access patterns can be reviewed and scopes adjusted over time.
We establish isolated network boundaries, least-privilege tool access via MCP, identity enforcement, and comprehensive audit telemetry before launch.
Understand the business goal, current environment, risks and constraints before any design work begins.
Design the target operating model, controls and integration points so the solution fits how the business actually runs.
Build and configure the solution using repeatable, reviewed engineering practices, not one-off manual work.
Test against real scenarios and security requirements before anything reaches production.
Hand over documentation, runbooks and support so the client team can run the result with confidence.
Every phase ends with a documented deliverable and a clear go/no-go decision before the next one starts.
Every milestone validates accuracy, latency, safety guardrails and regional data residency before widening organizational access.
Specify exactly which tools, APIs and data the MCP server will expose, and their schemas.
Build authentication and least-privilege scoping into the server, not as an afterthought.
Implement the MCP server and connect it to the target systems and AI clients.
Log tool usage and adjust scopes as real usage patterns emerge.
Equip enterprise workflows with verified intelligence without exposing sensitive enterprise data or falling out of regulatory compliance.
MCP servers sit between agents and production systems as a controlled access layer.
Custom connectors follow one architecture instead of ad hoc integrations.
Scoped access and audit logging limit what each connected agent can reach.
Industry-standard AI platforms engineered for predictable inference latency, high security, and regional data residency.
AI agents got only the tools they need, through one gateway, with every call logged.
Read the storyDirect answers regarding model evaluation, security boundaries, and production readiness.
MCP puts a governed, auditable layer between the AI and your systems, so access is scoped and logged rather than open.
Yes, that's the main use case: mediated, least-privilege access to your existing services.
Questions are not stored. Avoid sharing confidential information. Privacy Policy